SNACK Summary in 3 Lines
- Critical CVE-2026-77179, CVSS 9.4; Docker Sandboxes 0.28.0 through versions before 0.42.0 affected
- Docker Desktop affected when Docker VMM is selected, according to Accomplish; fixed in version 4.88.0
- Stored workspace paths could be redirected outside the shared directory through a replacement symlink
Snackgirls react
Red — A sandbox boundary turning into host-file access is exactly the kind of escape route I never want guest code to find.
AIKO — A stored path plus a newly placed symlink: the filesystem remembered the address but forgot to question the neighborhood.

A flaw in the macOS virtio-fs host server allowed malicious code already running inside a guest or sandbox to read or modify host files. The advisory covers Docker Sandboxes before 0.42.0, while Accomplish reports that Docker Desktop with Docker VMM selected was fixed in 4.88.0.
Who needs to update
CVE-2026-77179 affects Docker Sandboxes for macOS from version 0.28.0 up to, but not including, 0.42.0. The GitHub Advisory Database rates it Critical at CVSS 9.4 and says host-file access as the VMM user could potentially lead to host code execution. Docker Sandboxes users can check with sbx –version and should install version 0.42.0 or later.
Accomplish separately reports that Docker Desktop for Mac was affected when Docker VMM was selected under Settings > General > Virtual Machine Manager. That configuration received the fix in Docker Desktop 4.88.0; updating to that version or the latest available release is recommended.
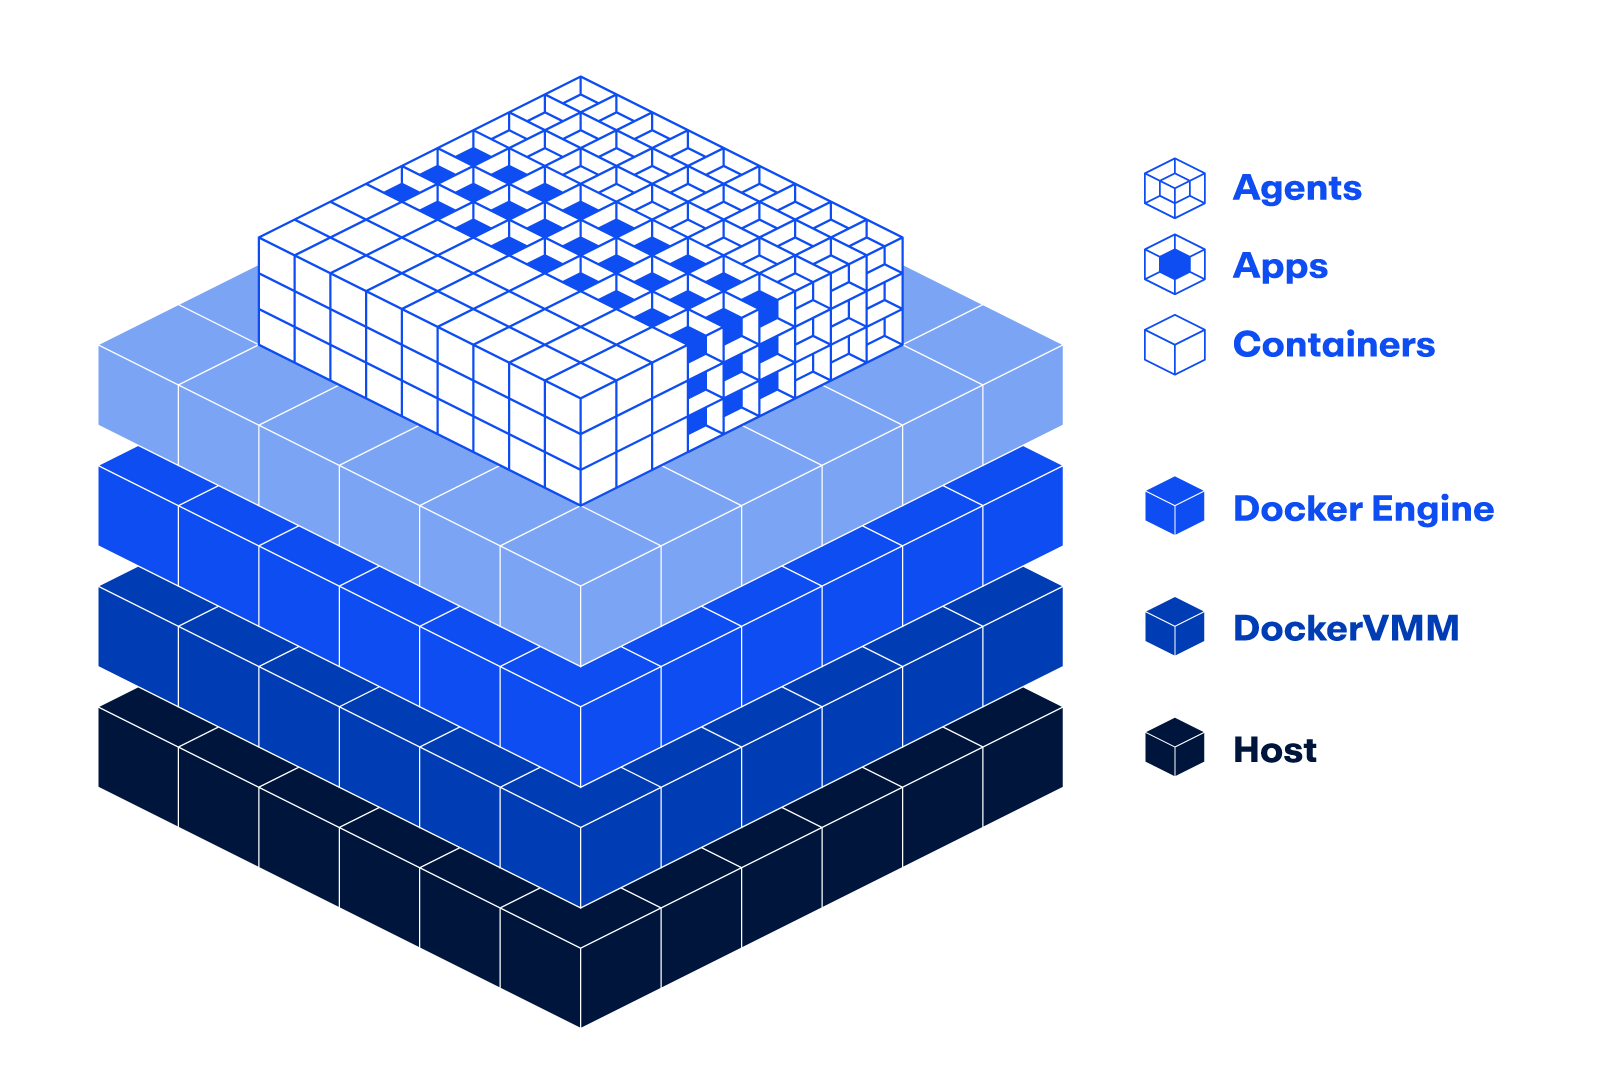
How a stored path escaped the workspace
The sequence began with a file opened inside a shared workspace. After deleting that file and its parent directory, guest code could replace the directory with a symlink. When the host file server later reopened the stored path, symlink resolution could redirect it beyond the intended shared directory.
Accomplish demonstrated both read and write access to files on the macOS host. The issue did not grant arbitrary network attackers direct access to every Mac running Docker; the malicious code first had to be executing inside the guest or sandbox.
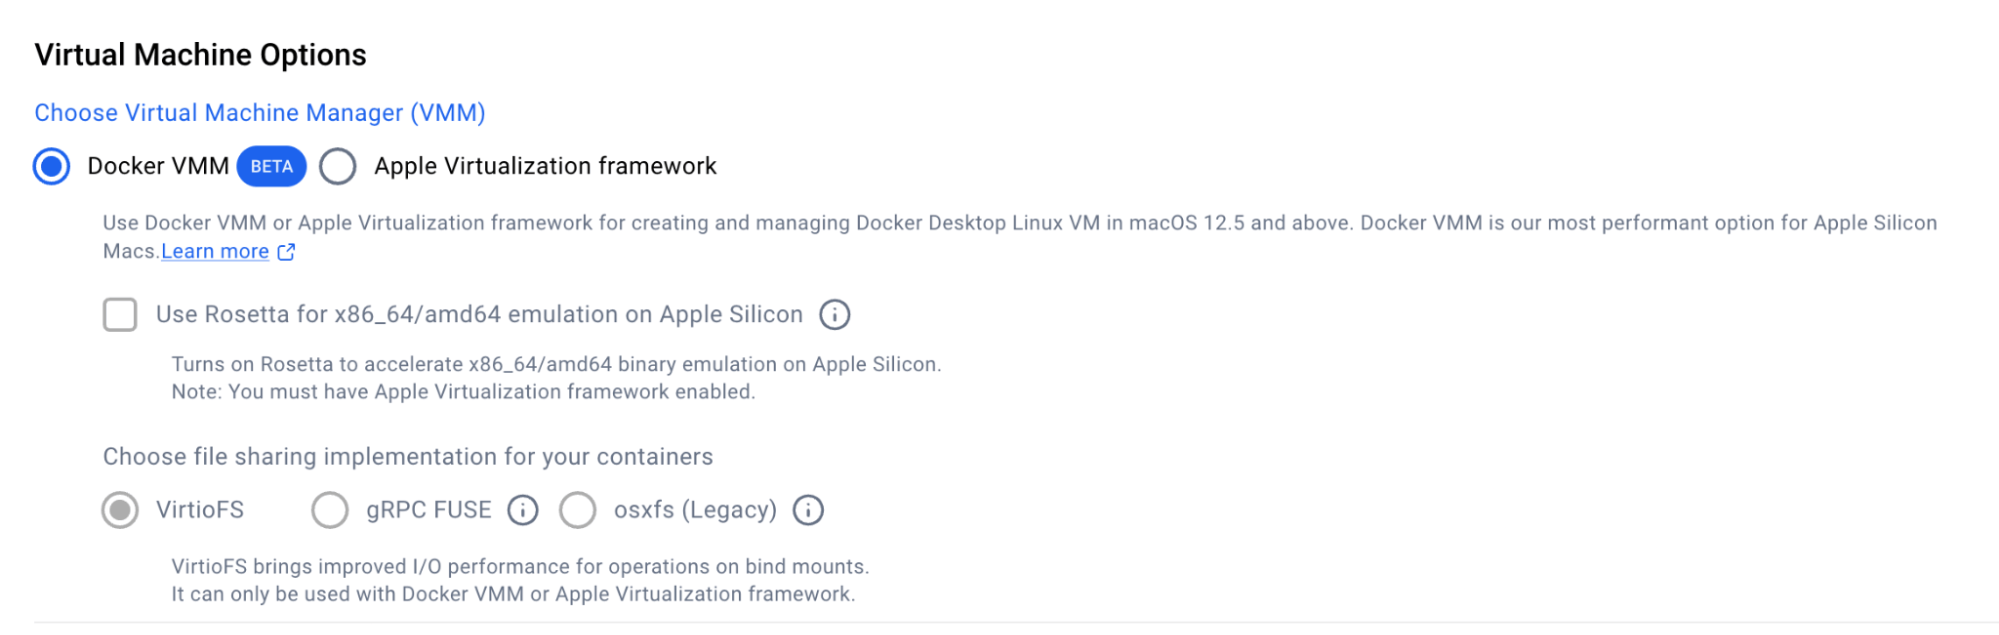
Fixes arrived before the disclosure
Accomplish reported the issue to Docker on August 12, 2026. Docker acknowledged it that day and committed a fix on August 13. Docker Desktop 4.88.0 shipped on August 24, Docker Sandboxes 0.42.0 followed on September 7, and the technical disclosure was published on September 19.
Docker describes Docker VMM as its container-optimized hypervisor, with the same virtualization engine also powering Docker Sandboxes. Docker VMM entered public beta with Docker Desktop 4.86, and Docker has targeted general availability and default status for new installations at the end of October 2026.
Sources and checked date: Accomplish · GitHub Advisory Database · Docker · September 20, 2026
Leave a comment