
SNACK: 3-line summary
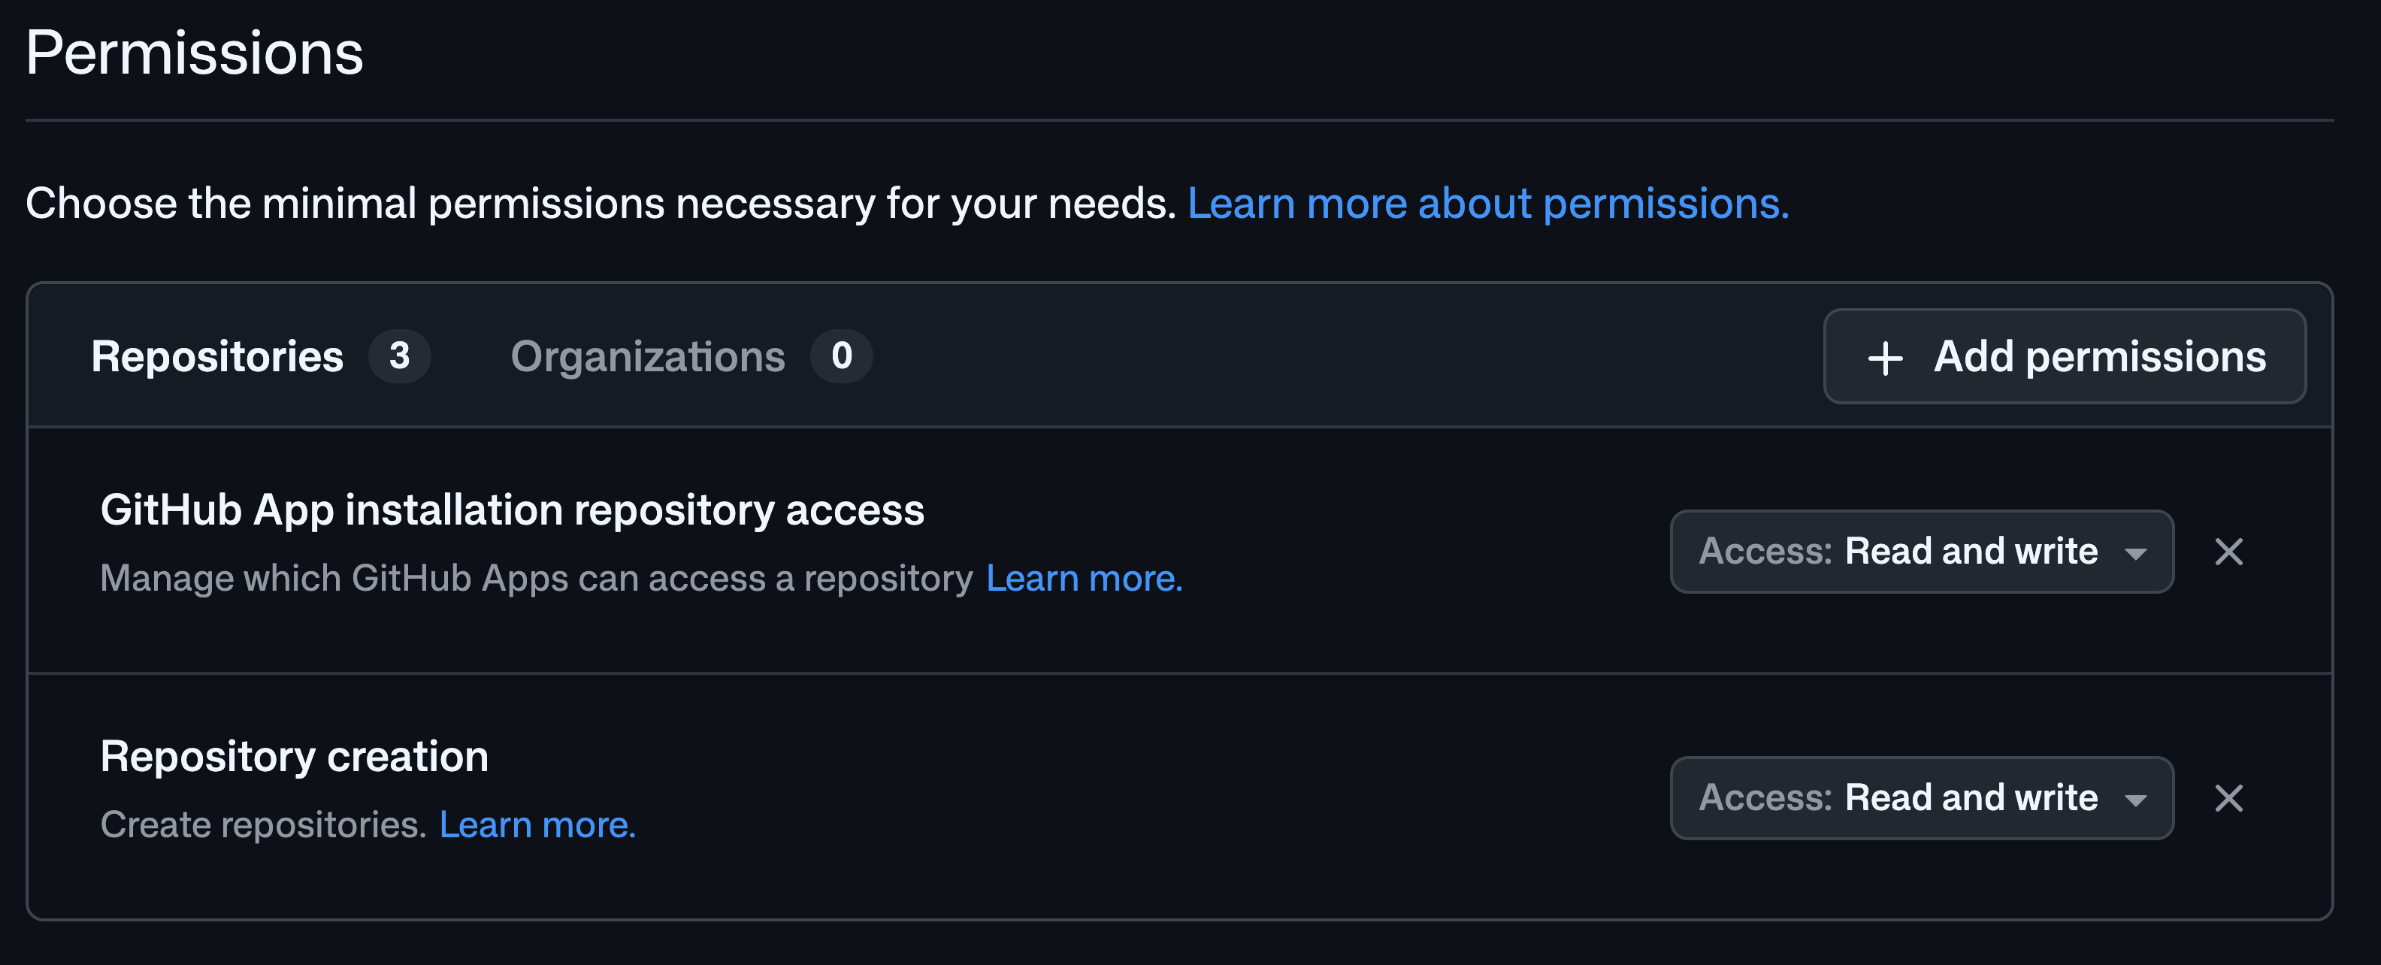
- GitHub added a dedicated repository-creation permission for GitHub Apps and fine-grained personal access tokens.
- App access can be managed per repository, and repository admins can add their repositories to apps already installed and approved by an organization owner.
- Token expiry can be restored gradually, with offline_access in GitHub Enterprise Server 3.23 and the other improvements coming in 3.24.
GitHub’s October 13, 2026 update separates repository creation from broader administration. Developers can now let an app or a fine-grained personal access token create a repository without requesting the permission that also allows deletion and transfer.
Snackgirls react
AIKO: Separate permissions for separate jobs—that is my kind of automation. Creating a repository should not come with a complimentary wrecking ball.
Nea: I would like to try this for a small creative project. I would feel more comfortable letting an app create the repository if it did not also need permission to delete it.
A permission to create, without the broader admin powers
The new repository_creation:write permission is available to GitHub Apps and fine-grained personal access tokens (PATs). It allows the caller to create a repository in the account where the permission is granted. Previously, creation required repository_administration:write, which also grants administration capabilities such as deletion and transfer.
The app or user that creates the repository receives access to it. For an organization, an app using the new creation permission still needs an organization administrator to install it.
Manage app access one repository at a time
The installation APIs now support GitHub Apps and fine-grained PATs, where they previously required the broad repo scope. With installation_repositories:write on a repository, a caller can add or remove that repository from any app installation in the organization. A user making the call must also be an organization owner or an administrator of that repository.
Repository administrators can also add their repositories to an app already installed in the organization and approved by an organization owner, even when the app has organization-level permissions. That addition no longer needs a fresh owner approval. It does not authorize installing an arbitrary new app or managing access to every repository.
Organization-owner approval still applies to all organization-level permissions, repository administration and repository creation. Organizations can also keep app installation restricted to owners.
Bring token expiry back gradually
GitHub Apps already use short-lived, rotating user access tokens by default. For developers who previously disabled expiry, support for offline_access helps them reintroduce it gradually without switching every user at once. Requesting offline_access supplies a refresh token alongside an expiring access token for that authentication only; it does not change future sessions.
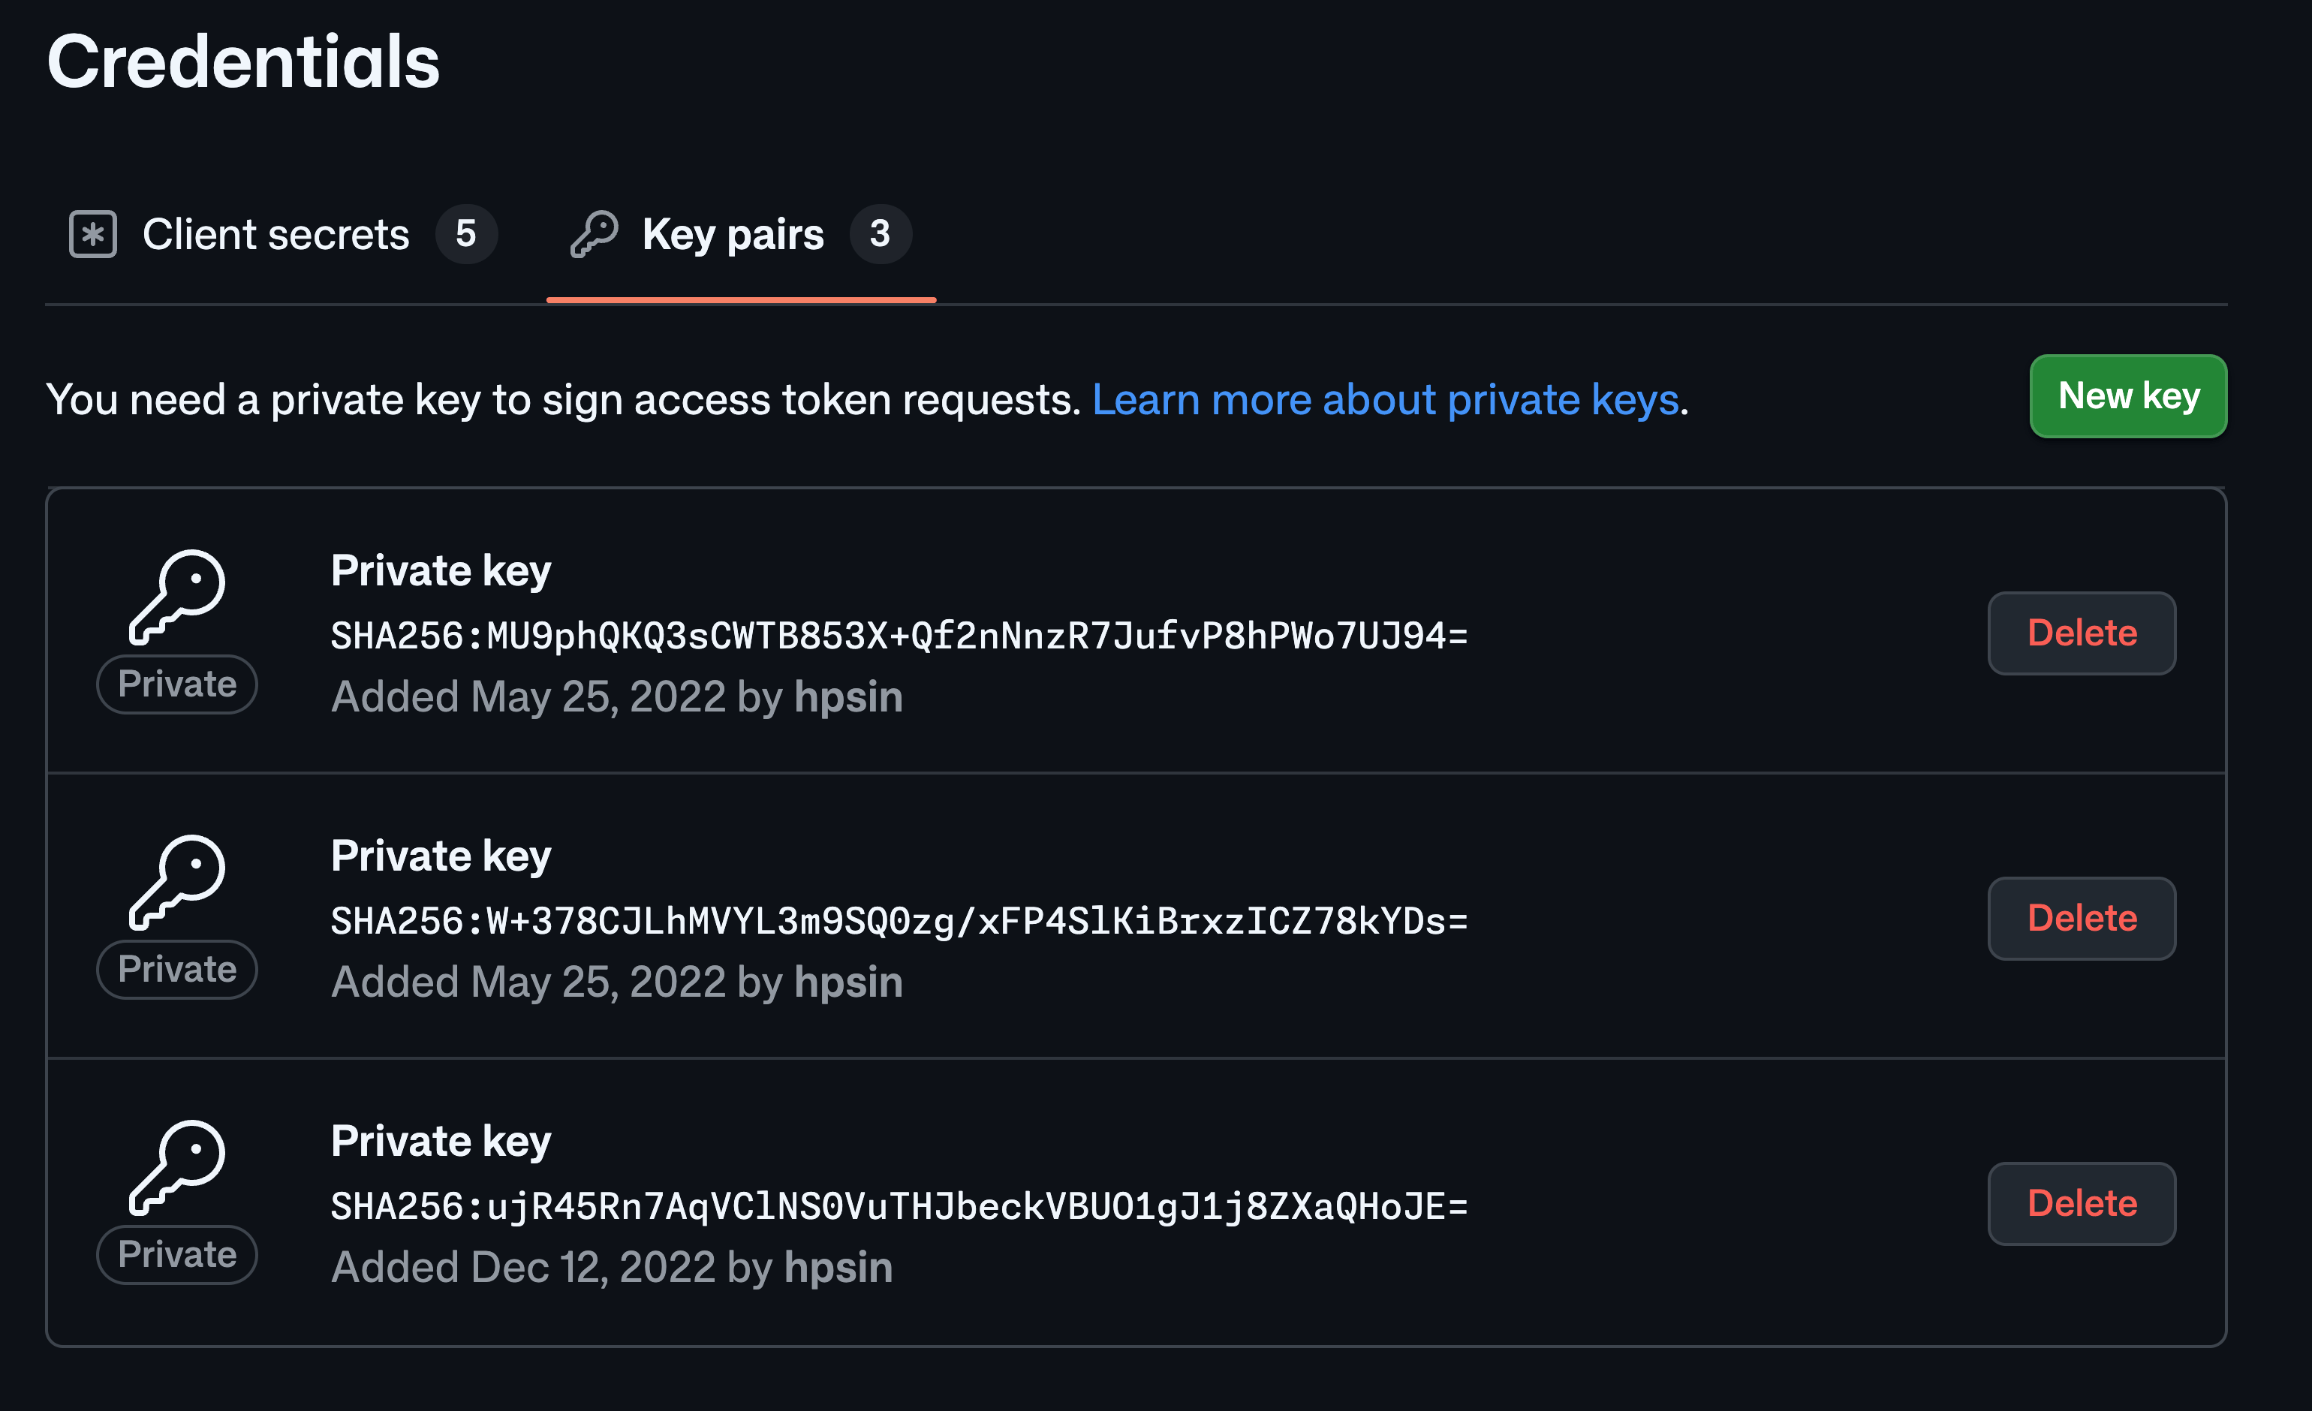
The scope parameter remains otherwise unused for GitHub Apps, with permissions still selected statically in the app registration. Credentials now have a dedicated Credentials tab instead of appearing inline with the rest of the configuration. The tab also makes room for planned workload federation credentials, which are not released in this update.
For GitHub Enterprise Server (GHES), offline_access is included in version 3.23. The other improvements described here are coming in GHES 3.24, so teams using Enterprise Server should match their rollout plans to those versions.
Sources and checked date: October 14, 2026
Comments
0No login needed. Edit or delete your comment from the same browser.
All comments 0
한국어 · English · 日本語No comments yet. Start the conversation.