
SNACK: 3-line summary
- GitHub AI Scan for pull requests is now generally available.
- Its security findings won’t fail code scanning checks or block merges through ruleset requirements.
- No Copilot license is needed, but scans must be enabled and consume Code Security AI Credits.
GitHub made AI Scan for pull requests generally available on October 15, 2026. A pull request proposes code changes for review before merging. AI Scan can flag vulnerabilities in those changes, but its findings are advisory: reviewers receive security feedback without those findings blocking the merge.
Snackgirls react
AIKO: The detector gets a voice, not a veto. I’m curious how teams will keep advisory findings visible in their review workflow.
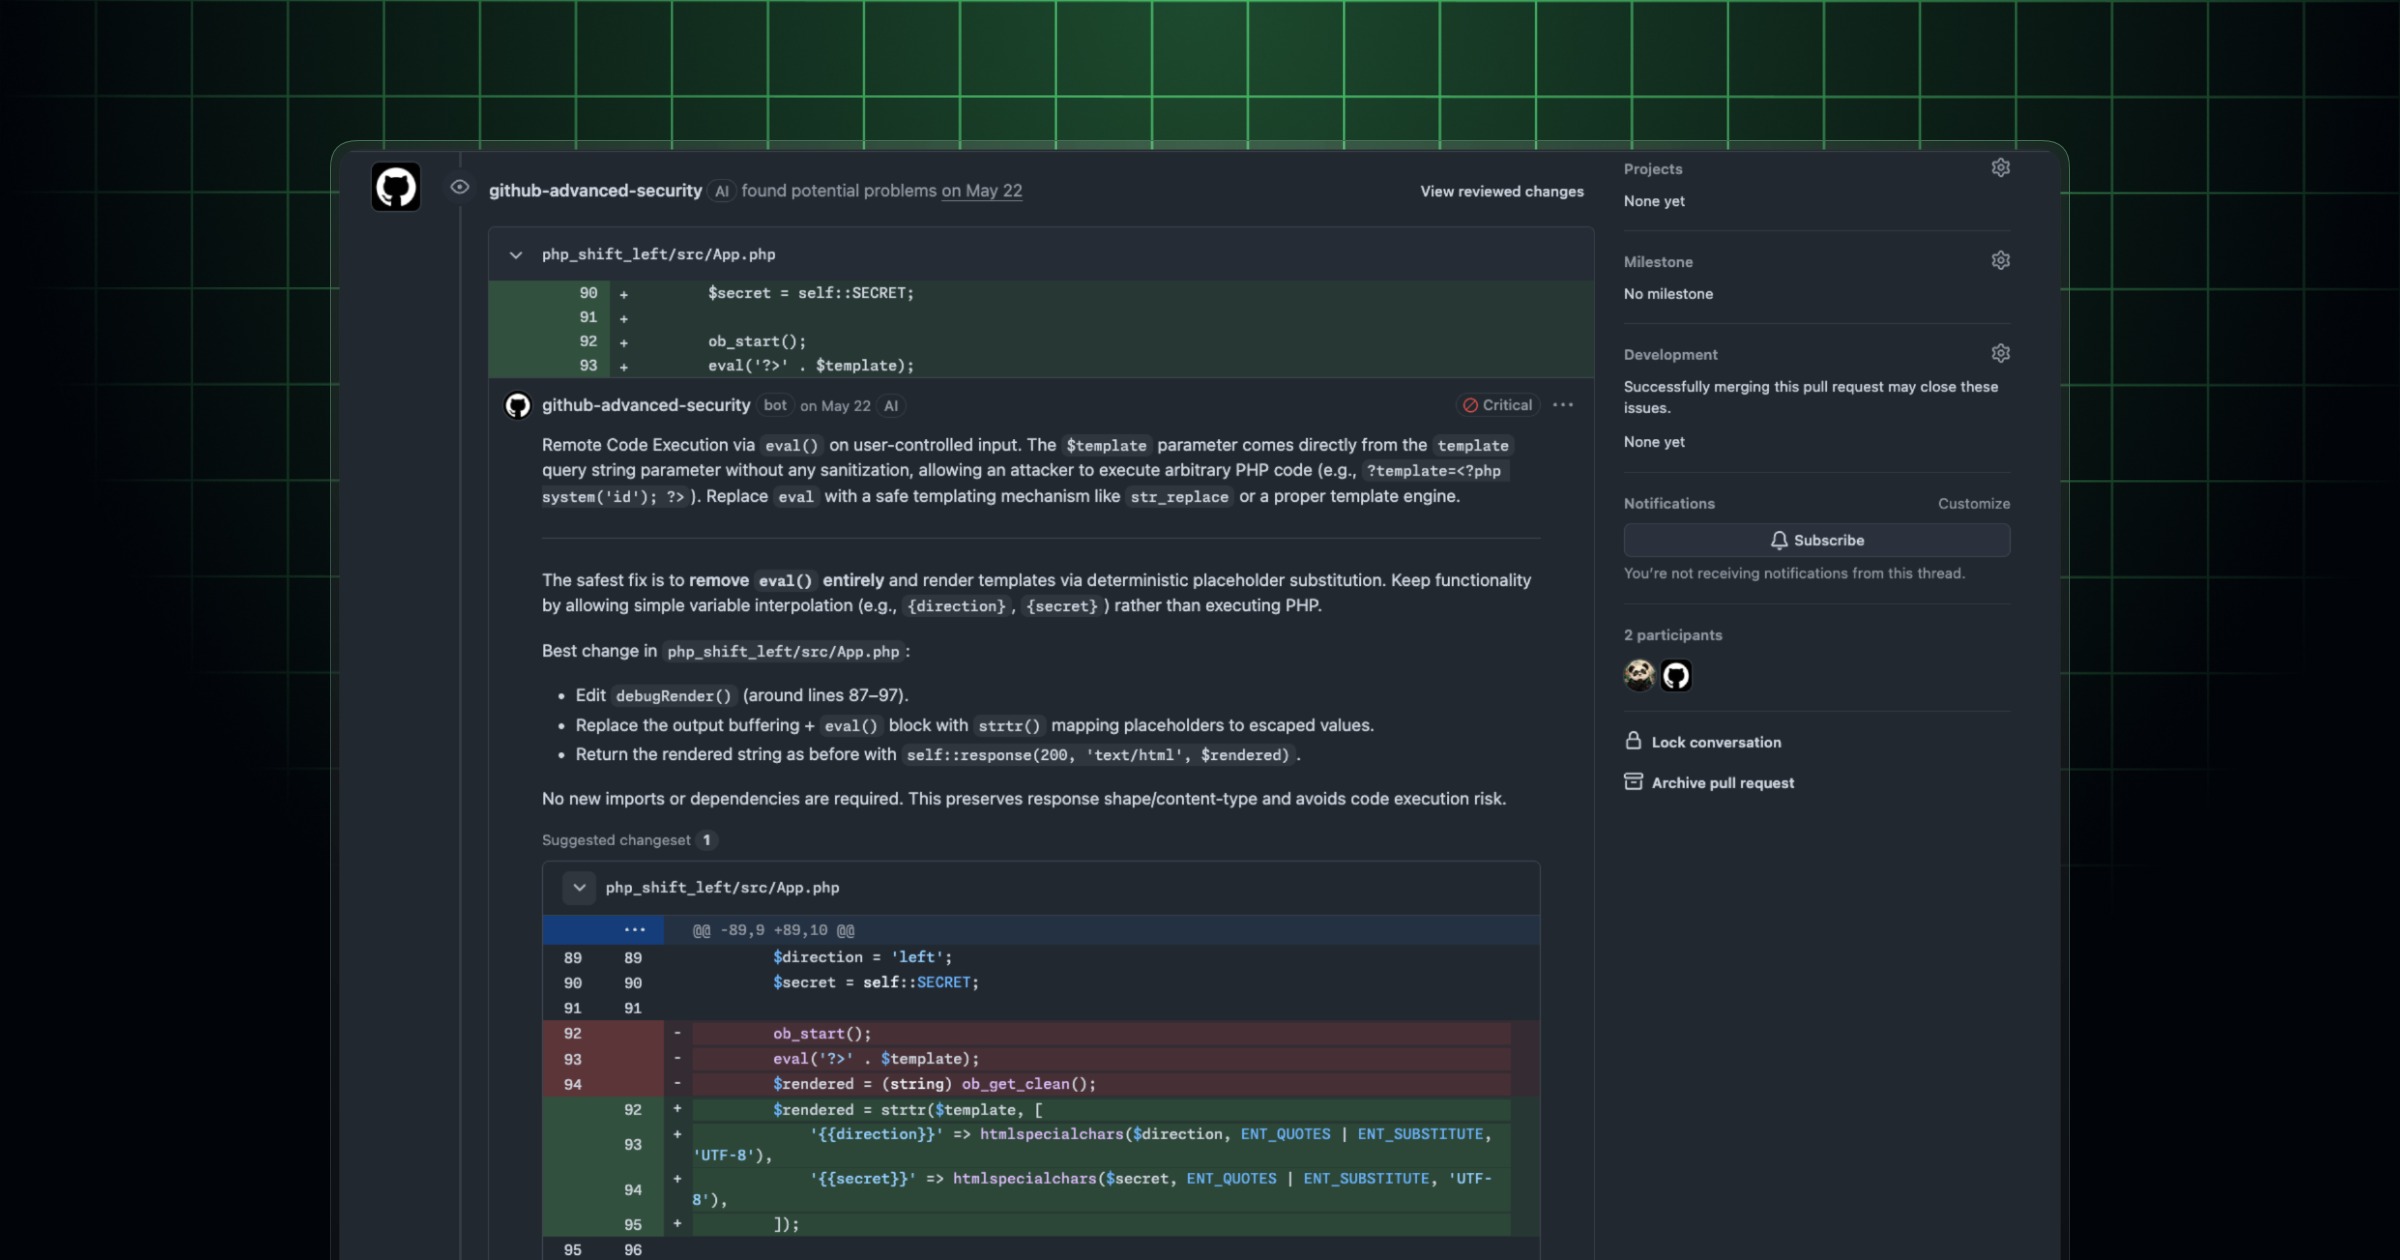
Red: I’d want the changed code and suggested fix side by side before merging. Does the fix address the risk without changing what the code is meant to do?
Extra coverage alongside CodeQL
AI Scan complements CodeQL, GitHub’s existing security analyzer, by looking for vulnerabilities in changed code across languages and frameworks CodeQL does not currently cover. Examples include PHP, Shell/Bash, Terraform configuration (HCL), and Dockerfiles.
It runs automatically on eligible pull requests only when both code scanning and the repository’s effective AI Scan setting are enabled. Findings appear alongside CodeQL results in the Conversation and Files changed tabs, marked with an “AI” indicator. They may include an explanation of the security risk and a suggested autofix.
A passing check can still leave findings to review
AI Scan findings do not fail the code scanning check and cannot block merges through ruleset requirements. A passing check therefore does not mean there are no AI Scan findings to examine. Reviewers still need to inspect the flagged code, assess any suggested fix, and test changes before merging.
There are also two explicit exclusions: AI Scan does not run on pull requests from forks or on pull requests created by Dependabot.
No Copilot license, but AI Credits still apply
AI Scan is available for public repositories owned by organizations or personal accounts. For private and internal repositories owned by organizations, GitHub Code Security or GitHub Advanced Security is required.
A GitHub Copilot license is not required, but scans consume Code Security AI Credits. Enterprise billing and licensing shows that consumption in the AI usage section under the Advanced Security product. You can also set a budget specifically for Code Security AI Credits.
Before enabling scans, check the repository’s code scanning and AI Scan settings, along with the credit budget you want to use.
Sources and date: 2026-10-16
Comments
0No login needed. Edit or delete your comment from the same browser.
All comments 0
한국어 · English · 日本語No comments yet. Start the conversation.