
SNACK: 3-line summary
- PHP has released fixes for two critical php2shell flaws that can allow unauthenticated remote code execution.
- WordPress operators need the server’s PHP runtime patched; updating themes or plugins alone is not enough.
- Cloudflare WAF protection adds a layer of defense but does not replace the PHP update.
The PHP project released security updates on October 21 for two critical vulnerabilities known as php2shell. If you operate a website, blog or shop running on PHP, update the server’s PHP runtime or ask your hosting provider to apply the fix.
Snackgirls react
AIKO: I’m interested in what the response reveals about a request. Blocking that reply still leaves a separate question: what has the server already done?
Nea: I can imagine a small-blog owner finishing the plugin updates and thinking the maintenance is done. I’d want to hear from the host that PHP itself has the fix, too.
The vulnerable code sits below WordPress
WordPress and Magento depend on PHP to process web requests. These flaws sit in that runtime, so updating the application, themes or plugins does not fix them. PHP’s advisory covers installations serving web requests, including PHP-FPM and Apache’s mod_php.
CVE-2026-109618 can cause request cleanup to use partially initialized internal data after an out-of-memory error. CVE-2026-109619 can leave stale internal state pointing to freed memory that a later request may use. Possible consequences include service disruption and data exposure as well as code execution.
Which PHP update to ask for
The releases fixing both vulnerabilities are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Use the fixed release for your supported branch or a vendor package containing the backported security fixes.
If a hosting provider manages PHP, ask it to apply the update or confirm that its package already contains the fixes. Linux distribution and LTS vendors received patches in advance, and a package’s displayed version number alone does not establish its backport status. Check the vendor’s security notice for the package you use.
PHP 8.1 and older no longer receive regular updates from the PHP project, so ask your vendor about backported fixes or upgrade to a supported branch. The project also supplied minimal source backports for PHP 7.4, 8.0 and 8.1; this does not restore regular support.
Where Cloudflare’s protection helps—and stops
Cloudflare says it has observed attack traffic targeting these vulnerabilities and has deployed default protections for Free and paid customers with its web application firewall (WAF) deployed. Free customers do not need to enable the new managed rules separately. Pro, Business and Enterprise customers should confirm that their Managed Ruleset is deployed in Block mode.
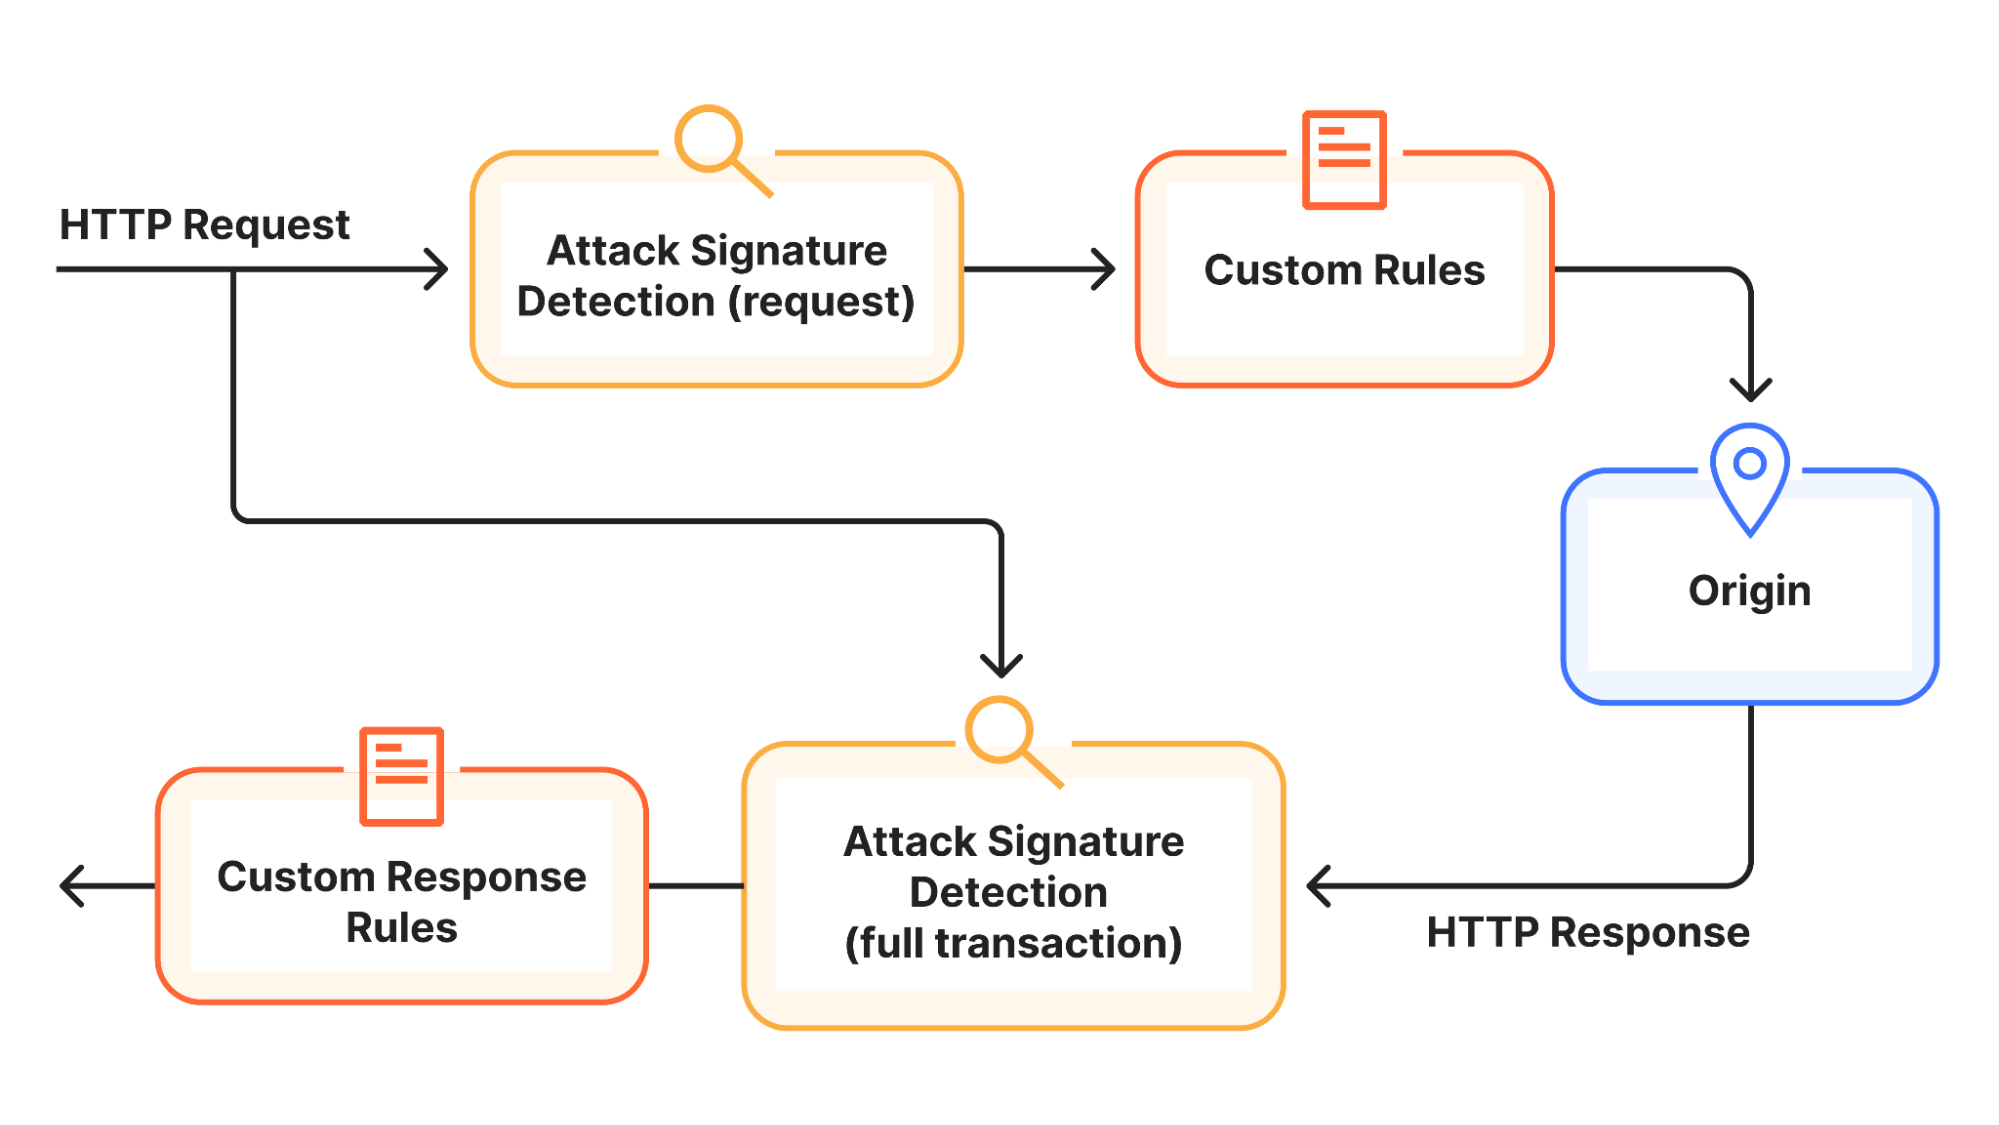
Its full transaction detection combines evidence from an HTTP request and the origin server’s response. A matching response rule can block that response before it reaches the requester, but it cannot undo actions already performed on the origin server. Keep WAF protection enabled while applying the PHP fix.
Sources and checked date: October 22, 2026
Comments
0No login needed. Edit or delete your comment from the same browser.
All comments 0
한국어 · English · 日本語No comments yet. Start the conversation.