
SNACK: 3-line summary
- Cloudflare has added traffic analytics and access controls for personal agents.
- Operators can allow supported agents, block them on pages with ads or block them outright.
- Account-linked views require Account Abuse Protection, which is currently in early access.
Cloudflare’s November 4 update lets site owners inspect personal-agent traffic and set access rules for supported agents. Those automated visits may come from customers asking an assistant to compare products, find support or make a purchase.
Snackgirls react
AIKO: A customer’s errand can look like bot traffic. My urge to classify everything just acquired another edge case.
Nea: I’d like to send an agent looking for an article about a game’s lore. Then I’d be wondering whether the site would let my research assistant through.
See where personal agents go—and where they get stuck
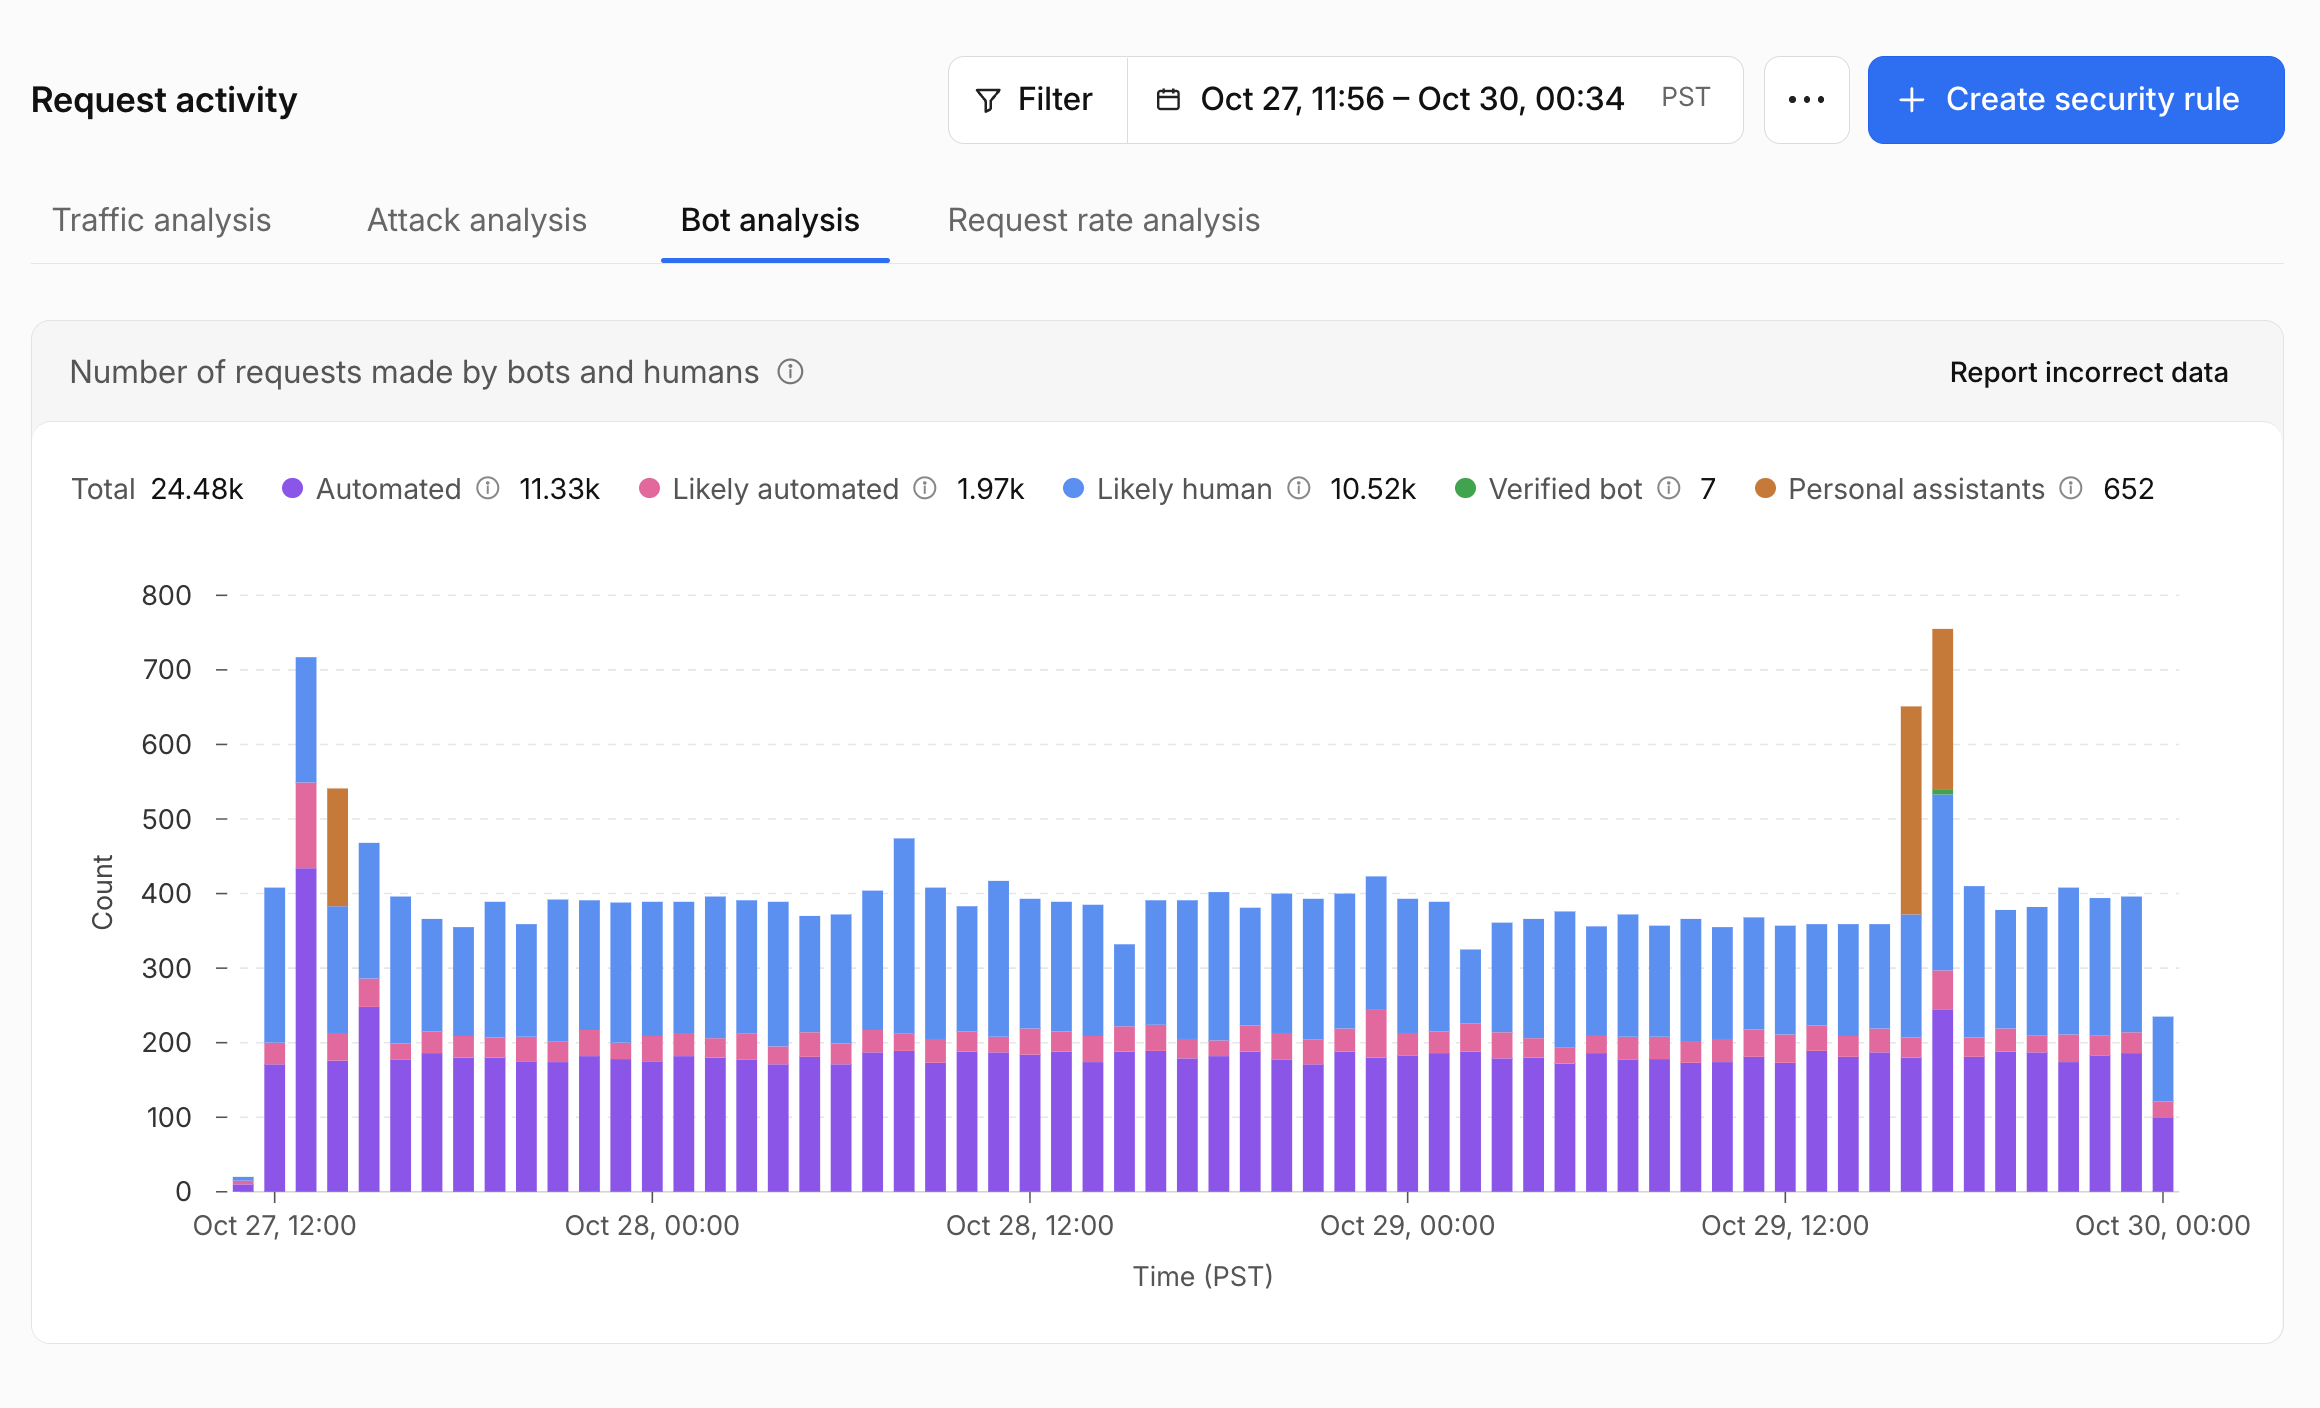
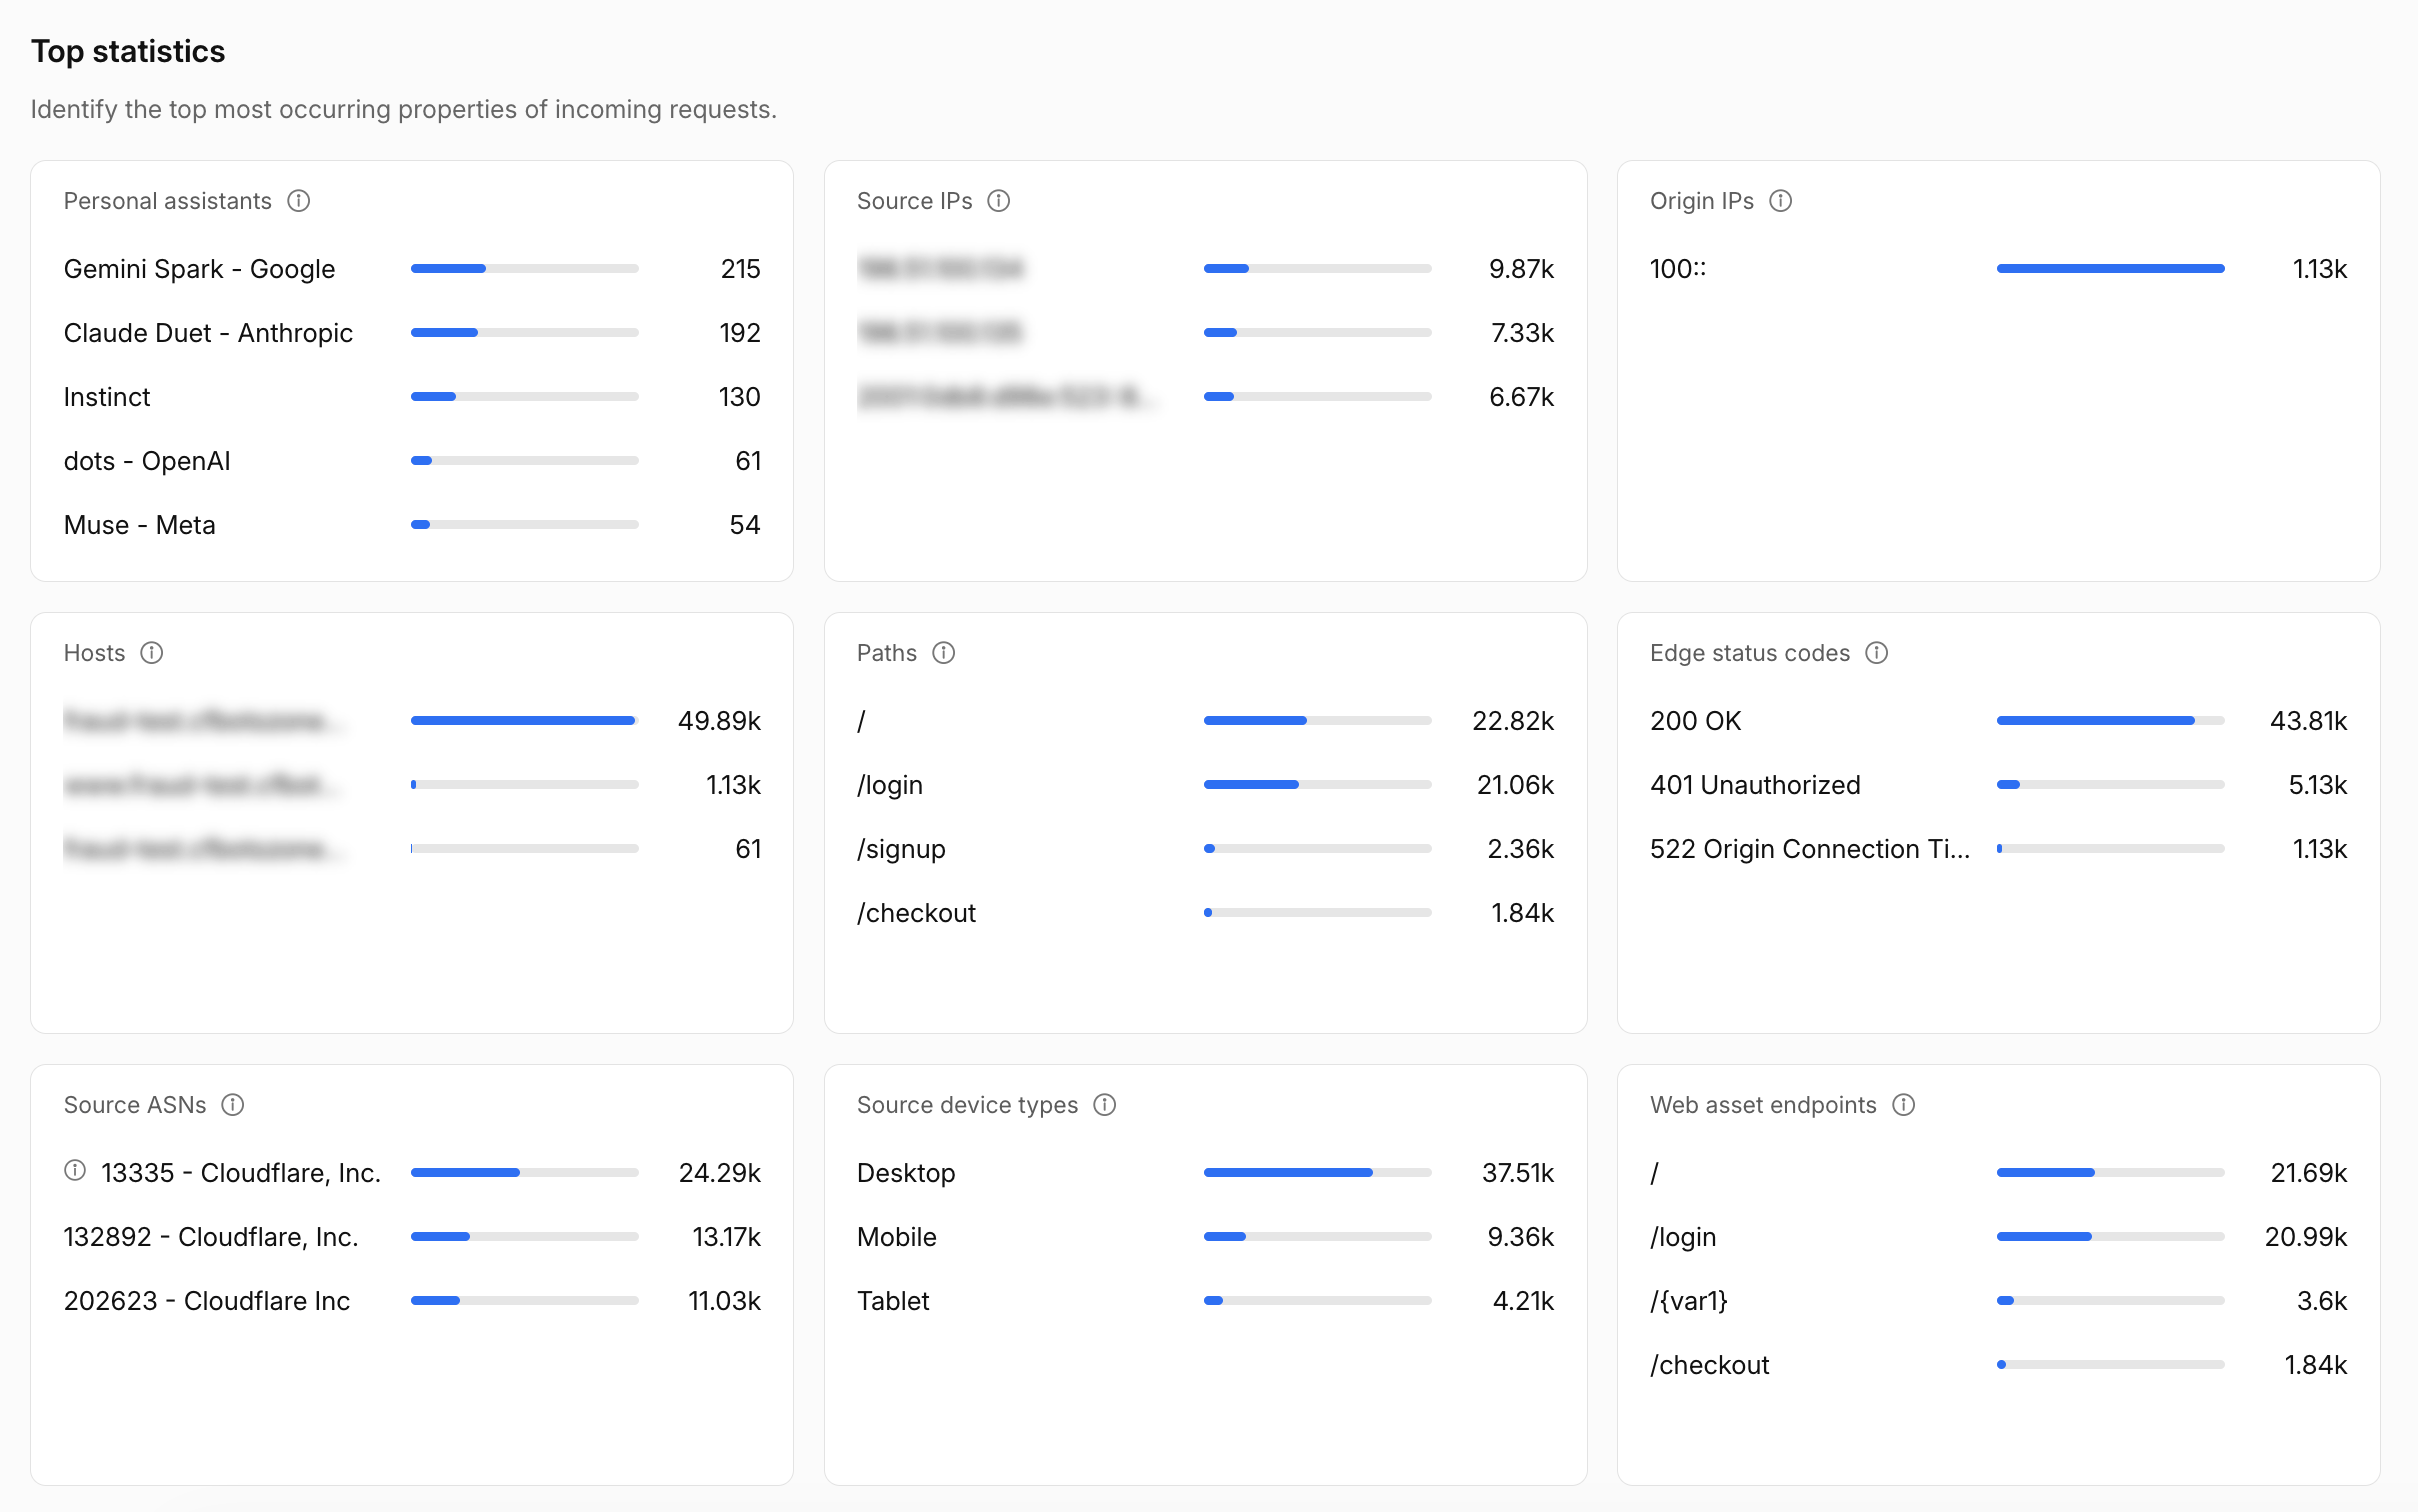
Security Analytics now includes a Personal Assistants category in its Bot Analysis chart, letting operators isolate that traffic over time. A new Personal Assistants widget in Top statistics lists visiting agents and their request counts.
Select an agent and the other widgets filter to its requested paths, response status codes and source networks. Operators can see whether it reaches product pages or checkout, or encounters errors on pages it cannot use.
Allow one agent while restricting others on ad-funded pages
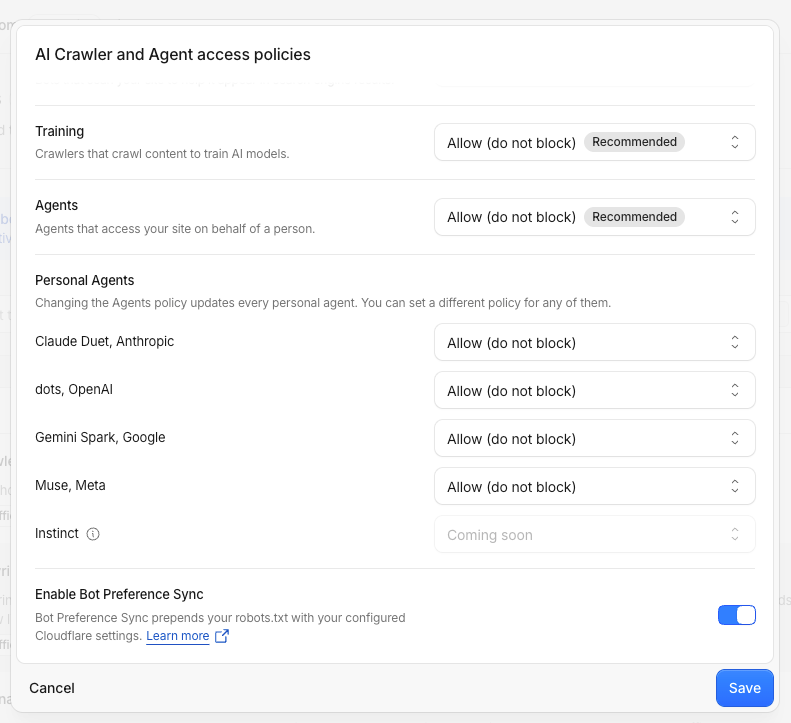
In Security Settings, the renamed AI Crawler and Agent access policies setting provides an overall Agents policy with individual overrides for supported personal agents. The three choices are Allow (do not block), Block on pages with ads, and Block.
Cloudflare illustrates this with an overall policy that blocks agents on pages with ads, then an allow exception for one supported agent. That lets an operator welcome the selected assistant while retaining ad-page restrictions for others. Existing Search and Training policies stay as they are.
Account-linked views require an early-access service
Sites using Account Abuse Protection, currently in early access, also get views linking agents to user accounts and agent details on login and sign-up events. An account overview helps fraud analysts distinguish a familiar agent from one appearing for the first time.
If an attacker appears to be using an agent on an account, analysts can target that account with a WAF rule on its Hashed User ID. They do not have to block the agent for everyone else who uses it.
Richer context remains a future goal: whether someone is an existing customer, what they authorized an agent to do, or whether they have a subscription. The new analytics alone do not establish those details. Cloudflare says carrying that context through agents will require further privacy-aware work on user context, reputation and accountability.
Sources and checked date: November 5, 2026
Comments
0No login needed. Edit or delete your comment from the same browser.
All comments 0
한국어 · English · 日本語No comments yet. Start the conversation.