
SNACK Summary in 3 Lines
- Cloudflare’s scanned cohort: HelloRetryRequest rate down from about 52% to 3.7%
- X25519MLKEM768 prioritized when the origin supports the post-quantum hybrid
- Default-on optimization for new TLS 1.3 connections from Cloudflare to origins

Snackgirls react
Red — Cutting an entire back-and-forth out of a fresh connection is the kind of optimization you can picture immediately. One less detour—clean.
AIKO — Probe first, predict second, and roll back when the connection objects. Even robots appreciate an optimization with an exit strategy.
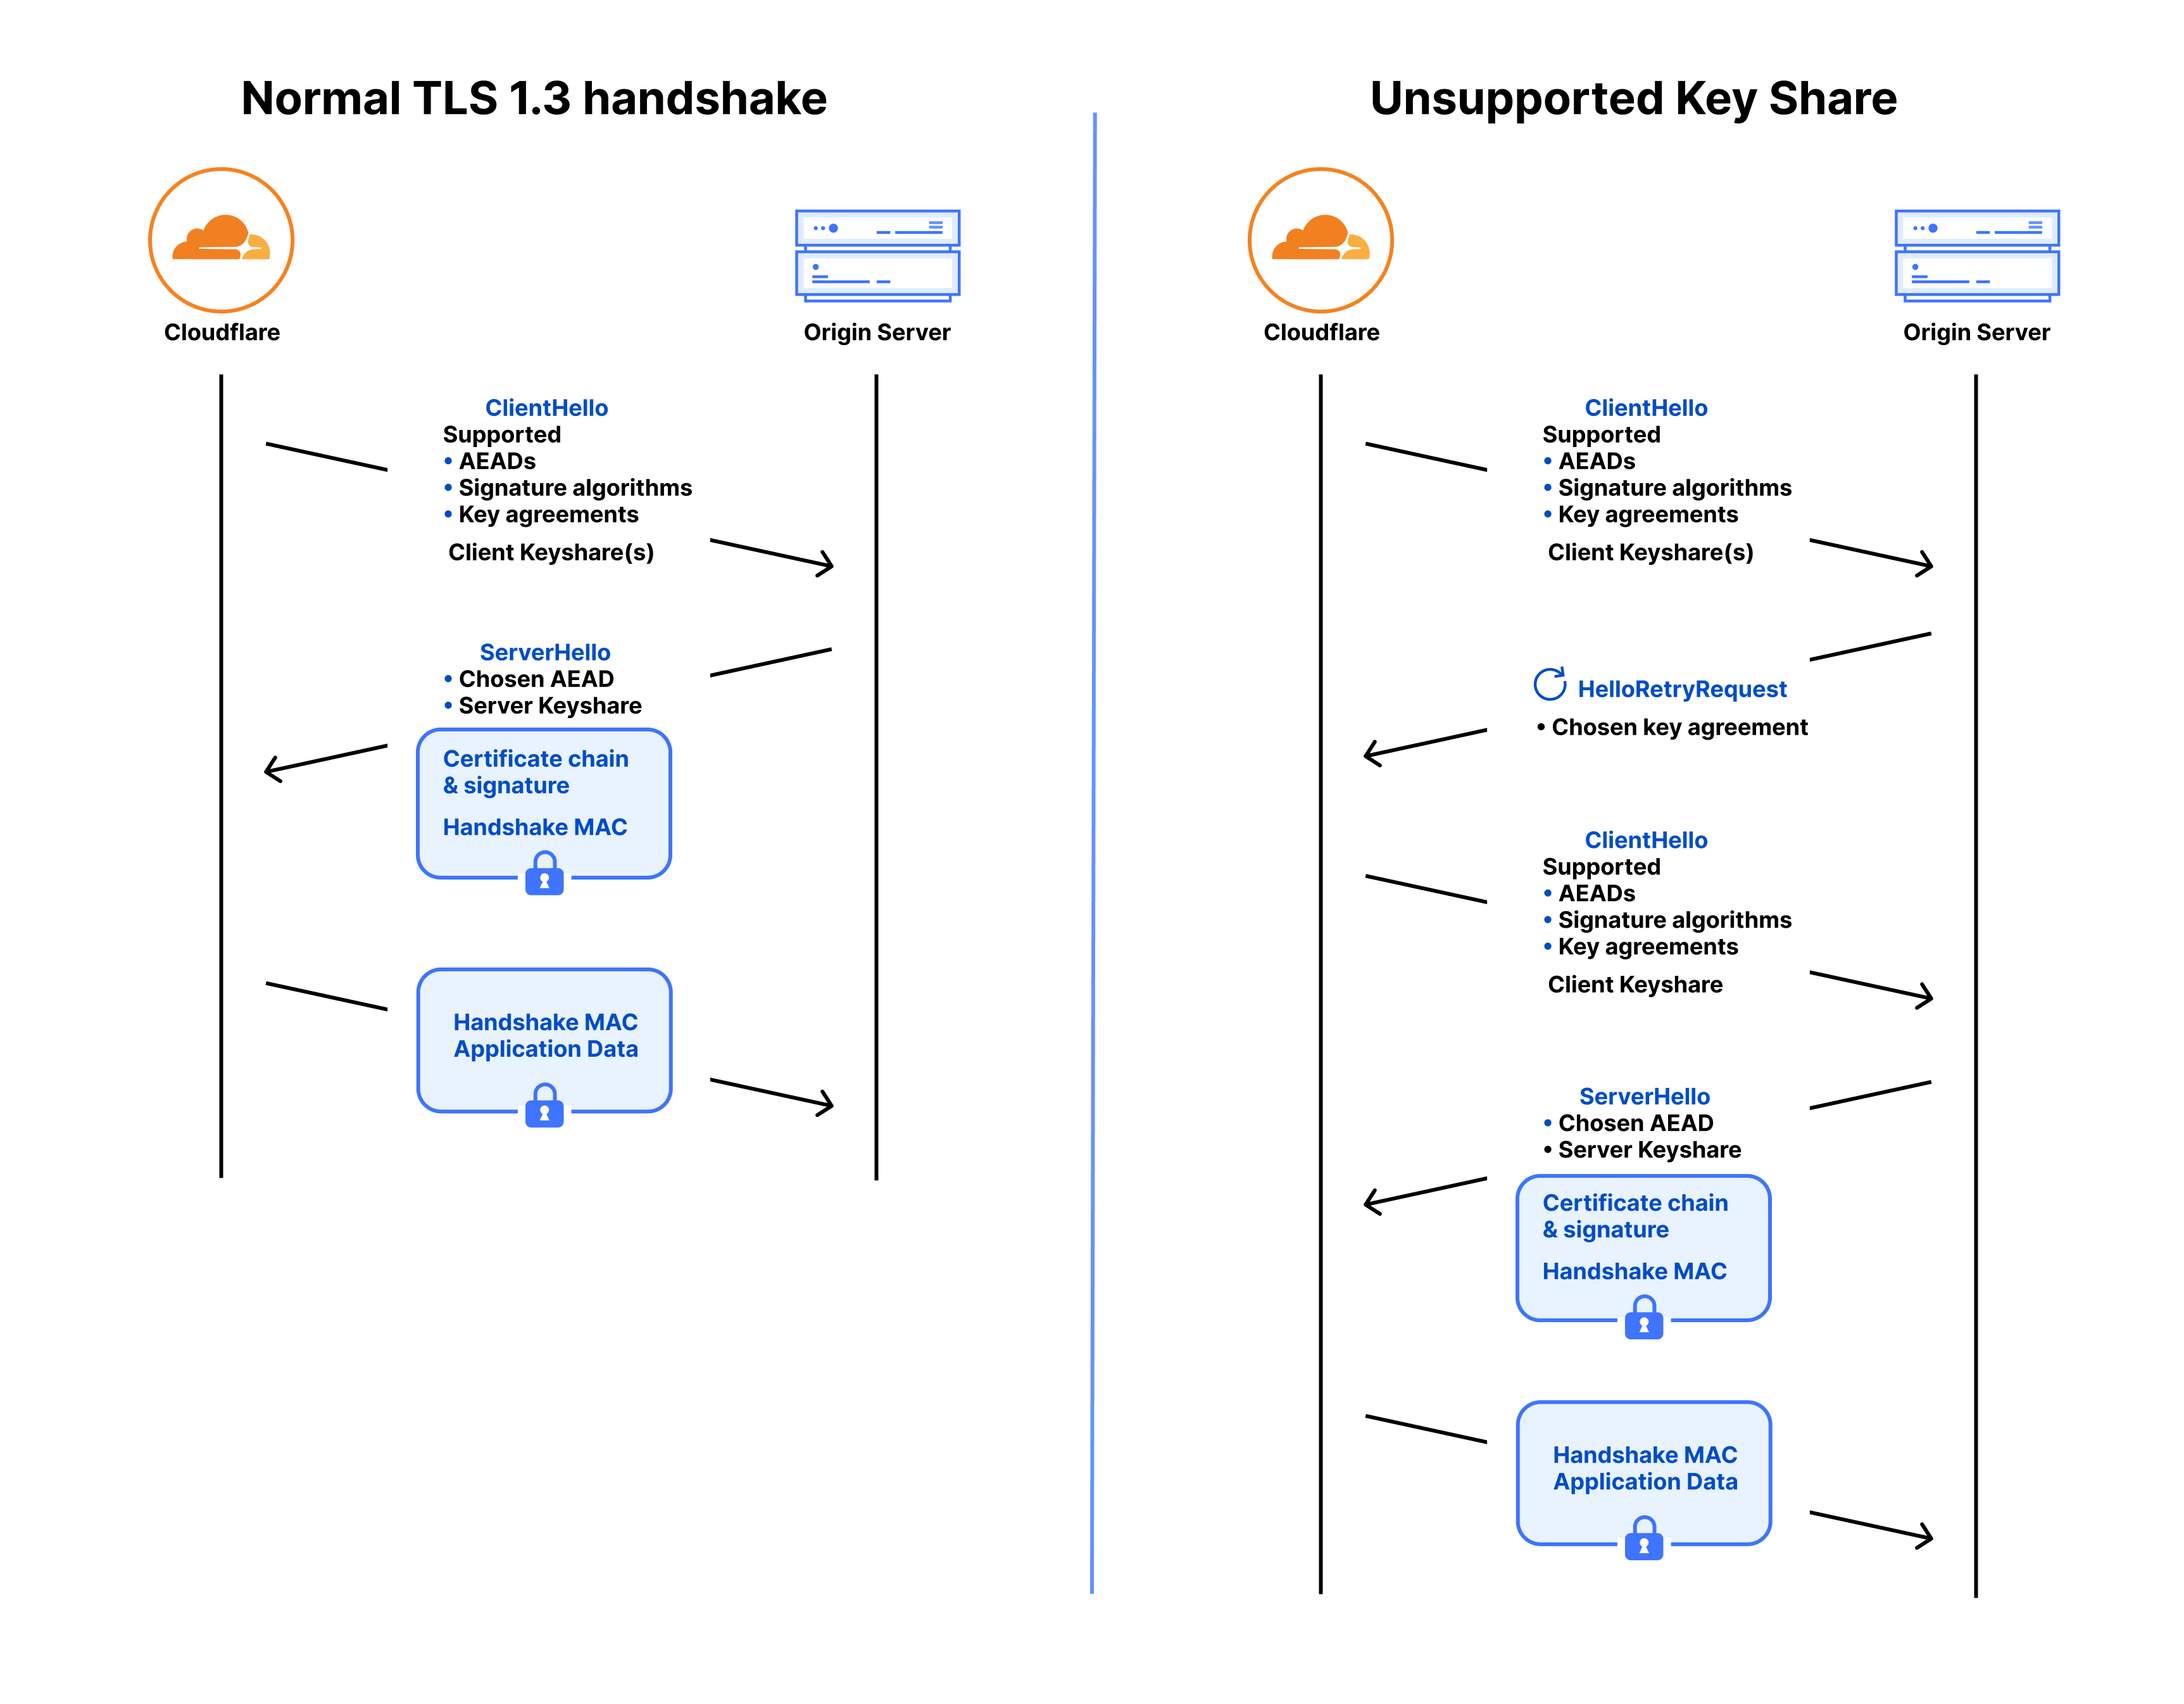
Cloudflare says Automatic Key Exchange lowered the share of origin connections requiring a HelloRetryRequest from about 52% to 3.7% in its scanned cohort. The system measures each origin’s supported and preferred key-agreement algorithms, predicts the right key share for the initial TLS 1.3 ClientHello, and usually avoids the extra round trip.
Removing a round trip from the origin handshake
If the key share in a TLS 1.3 ClientHello is not supported by the origin, the server can request another attempt through HelloRetryRequest. Automatic Key Exchange probes the origin first, allowing Cloudflare to send a more likely match on the initial connection.
Cloudflare reports that eliminating this retry reduced p90 handshake latency by more than 150 milliseconds for the affected origins. The measurement covers new TLS 1.3 connections between Cloudflare and origin servers—not the browser-to-Cloudflare leg or requests already using a keep-alive connection.
Post-quantum selection follows origin support
When an origin supports it, Cloudflare prioritizes the standardized post-quantum hybrid X25519MLKEM768. Otherwise, the system chooses a supported classical method. Cloudflare says 99.2% of post-quantum TLS 1.3 connections in the currently scanned cohort now finish in one round trip, while daily post-quantum origin traffic in that cohort has risen from about 25 billion to 45 billion connections.
The scanning pipeline has assigned preferences to well over one million domains. In the initial cohort, roughly 64% remained on X25519, about 33% selected X25519MLKEM768, and 3% used another classical curve. Origins are rescanned approximately every 24 hours, with changes introduced in stages and rolled back when connection failures or retry rates indicate trouble.

Default on, with limits operators should know
Automatic Key Exchange is enabled for existing Cloudflare zones and is on by default for new ones, so most users do not need to configure it. It applies when a zone uses Full, Full (strict), or Strict (SSL-Only Origin Pull) and the origin negotiates TLS 1.3. Cloudflare Tunnel is outside this system because it uses a separate post-quantum connection.
The dashboard also offers optional post-quantum-hybrid and FIPS compliance restrictions. Cloudflare warns that forcing the hybrid requirement on an origin without X25519MLKEM768 support can leave the two sides without a shared algorithm and cause TLS 1.3 connections to fail.

Sources and checked date: Cloudflare Blog · Cloudflare documentation · September 9, 2026
Comments
0No login needed. Edit or delete your comment from the same browser.
All comments 0
한국어 · English · 日本語No comments yet. Start the conversation.